Universal authorisation
Universal data authorization
Write-once, enforce-everywhereDefine access policies once. Orbital enforces them consistently wherever your data is accessed - across APIs, databases, streams and MCP.
Keep one set of rules
One policy governs APIs, databases, streams and MCP.
Decide access on real context
Make access decisions based on the caller, their role and claims, the request, and the data involved.
Mask fields, not whole responses
Mask individual fields by caller and context - so agents get the data they need without exposing sensitive values.
Prove exactly what was accessed
Trace every request from caller to response - including the systems accessed, policies applied, and where every returned value came from.
Authorize by data type
Define a rule for DateOfBirth once.
Orbital enforces it whether the underlying field is dob, date_of_birth or birthDate, and whether the value comes from an API, database, stream or MCP response.
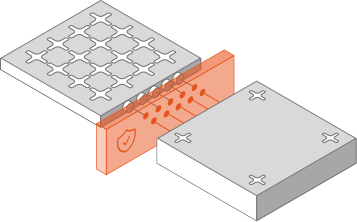
Write once. Enforce everywhere.
Field level enforcement
Control access to individual types and fields. Mask, filter or deny sensitive data based on the caller and the context of the request.
Every source, every path
The same rules are enforced across APIs, databases, Kafka streams, endpoints and MCP.
Policies as code
Version, review and deploy policies from Git. A single change is applied consistently wherever the protected data is used.
Authorization with real context
Policies can depend on more than roles and claims. Orbital can fetch the data needed to make an access decision — from team membership and entitlements to whether a customer has accepted the latest terms.
Decisions are evaluated against live data, at query time.
Give different roles different views of the same data. Managers can see the full record, while other users see only what their role allows.
Mark a data type as sensitive once, and mask it consistently wherever it appears - in APIs, database results, streams and more.
Serve different versions of the same event to different consumers. Managers can receive the full payload while restricted fields are removed for everyone else.
Use live data from other systems when making an access decision. This policy blocks restricted records entirely, while masking sensitive fields for everyone else.
policy OnlyManagers against EmployeeInfo (user : User) -> { read { when { // Managers can see everything user.groups.contains('Manager') -> EmployeeInfo // Users can see everything except salary user.groups.contains('User') -> EmployeeInfo as { ... except { salary } } // Everyone else gets an error else -> throw((NotAuthorizedError) { message: 'Not Authorized' }) } }}// Define some PIItype FirstName inherits String, PIItype LastName inherits String, PII
// Now secure it// Anything that serves PII data (API calls, db queries, kafka streams)// has this policy applied against itpolicy MaskPiiData against PII (user: User) -> { read { when { // Admins see everything: user.roles.contains('ADMIN') -> PII // ...otherwise mask it else -> concat(left(PII,3), '****') } }}// The eventmodel StockTradeEvent { symbol : Symbol price: Price customerName : CustomerName}
// A policy to secure itpolicy FilterCustomerFromTrade against StockTradeEvent (user: User) -> { read { when { // Managers see everything user.roles.contains('MANAGER') -> StockTradeEvent // Everyone else has customer hidden else -> StockTradeEvent as { ... except { customerName } } } }}
// Now stream it securelystream { StockTradeEvent }// Access Control Policy// Implements three-tier access:// 1. Managers: Full access to all trade data// 2. Restricted company trades: No access (filtered out)// 3. Standard users: Limited access with hidden customer and quantitypolicy FilterCustomerFromTrade against StockTradeEvent ( trade: StockTradeEvent, user: User, sensitiveCompanies: SensitiveCompanyList) -> { read { when { // TIER 1: Manager access - full visibility user.roles.contains('MANAGER') -> StockTradeEvent
// TIER 2: Restricted company filter // Removes entire trade record if trading entity is classified sensitiveCompanies.companies.contains(trade.tradingEntity) -> null
// TIER 3: Standard access // Shows trade but hides sensitive fields else -> StockTradeEvent as { ... except { tradingEntity, tradedQuantity } } } }}
Easily the best decision I’ve made was building our startup on Orbital. We got our platform built and operational in record time, with data pipelines and bespoke APIs for connecting our client data feeds.
The Orbital partnership was really easy. Their data platform made ingesting and performing complex data transformations simple.
The team were great to work with, and were able to quickly enhance the platform where required to suit our use case.
Frequently asked questions
Got another gnarly question? We’d love to hear it. Come and chat on Slack.
Secure your data, wherever it comes from.
Define a policy once. Orbital enforces it everywhere - every API, stream, store, and whatever comes next